
http请求头获取请求链接
File Request Links is a new feature we implemented which allows users to receive files from one-time collaborators. This was also an interesting engineering challenge that I’d like to explore in this article, particularly because it showcases many of the basic building blocks of a secure sharing process. First I’ll discuss what the feature is and then I’ll demonstrate the cryptographic design process behind it in small, iterative steps.
文件请求链接是我们实施的一项新功能,该功能使用户可以从一次性协作者那里接收文件。 这也是我在本文中要探讨的有趣的工程挑战,特别是因为它展示了安全共享过程的许多基本构建块。 首先,我将讨论该功能是什么,然后我将以较小的迭代步骤演示其背后的密码设计过程。
功能 (The Feature)
The basic idea is that we already let users send files to anyone. Using our share links, users can create links to content they have uploaded to Tresorit, and send them to people they want to grant access to with optional password protection.
基本思想是我们已经允许用户将文件发送给任何人。 使用我们的共享链接,用户可以创建指向已上传到Tresorit的内容的链接,并将其发送给想要通过可选密码保护授予访问权限的人员。
File Request Links work similarly; you create a link that you send to people you want to receive files from. You can also request email verification in case you want to receive uploads from multiple people and you want to connect each file to the uploader (or their email addresses at least).
文件请求链接的工作原理类似; 您创建一个链接,该链接发送给您要从中接收文件的人。 如果您希望接收来自多个人的上载,并且希望将每个文件都连接到上载者(或至少他们的电子邮件地址),则也可以请求电子邮件验证。
Example use cases:
用例示例:
- Law firms requesting confidential data 律师事务所要求提供机密数据
- Inbox for bids on open contracts 收件箱中未结合同的投标
- “Dead drop” for journalists receiving data
接收数据的记者的“ 死角 ”
- HR receiving CVs for open job offers 人力资源接受职位空缺的简历
要求 (The Requirements)
When engineering a feature like this, it’s very important to have your requirements laid out before you actually start planning any details, to ensure it will fit in with the overall product and that it will give users the same guarantees your software does everywhere else.
当设计这样的功能时,在实际开始计划任何细节之前先列出您的要求非常重要,以确保它适合整个产品,并为用户提供相同的保证,即您的软件在其他任何地方都可以使用。
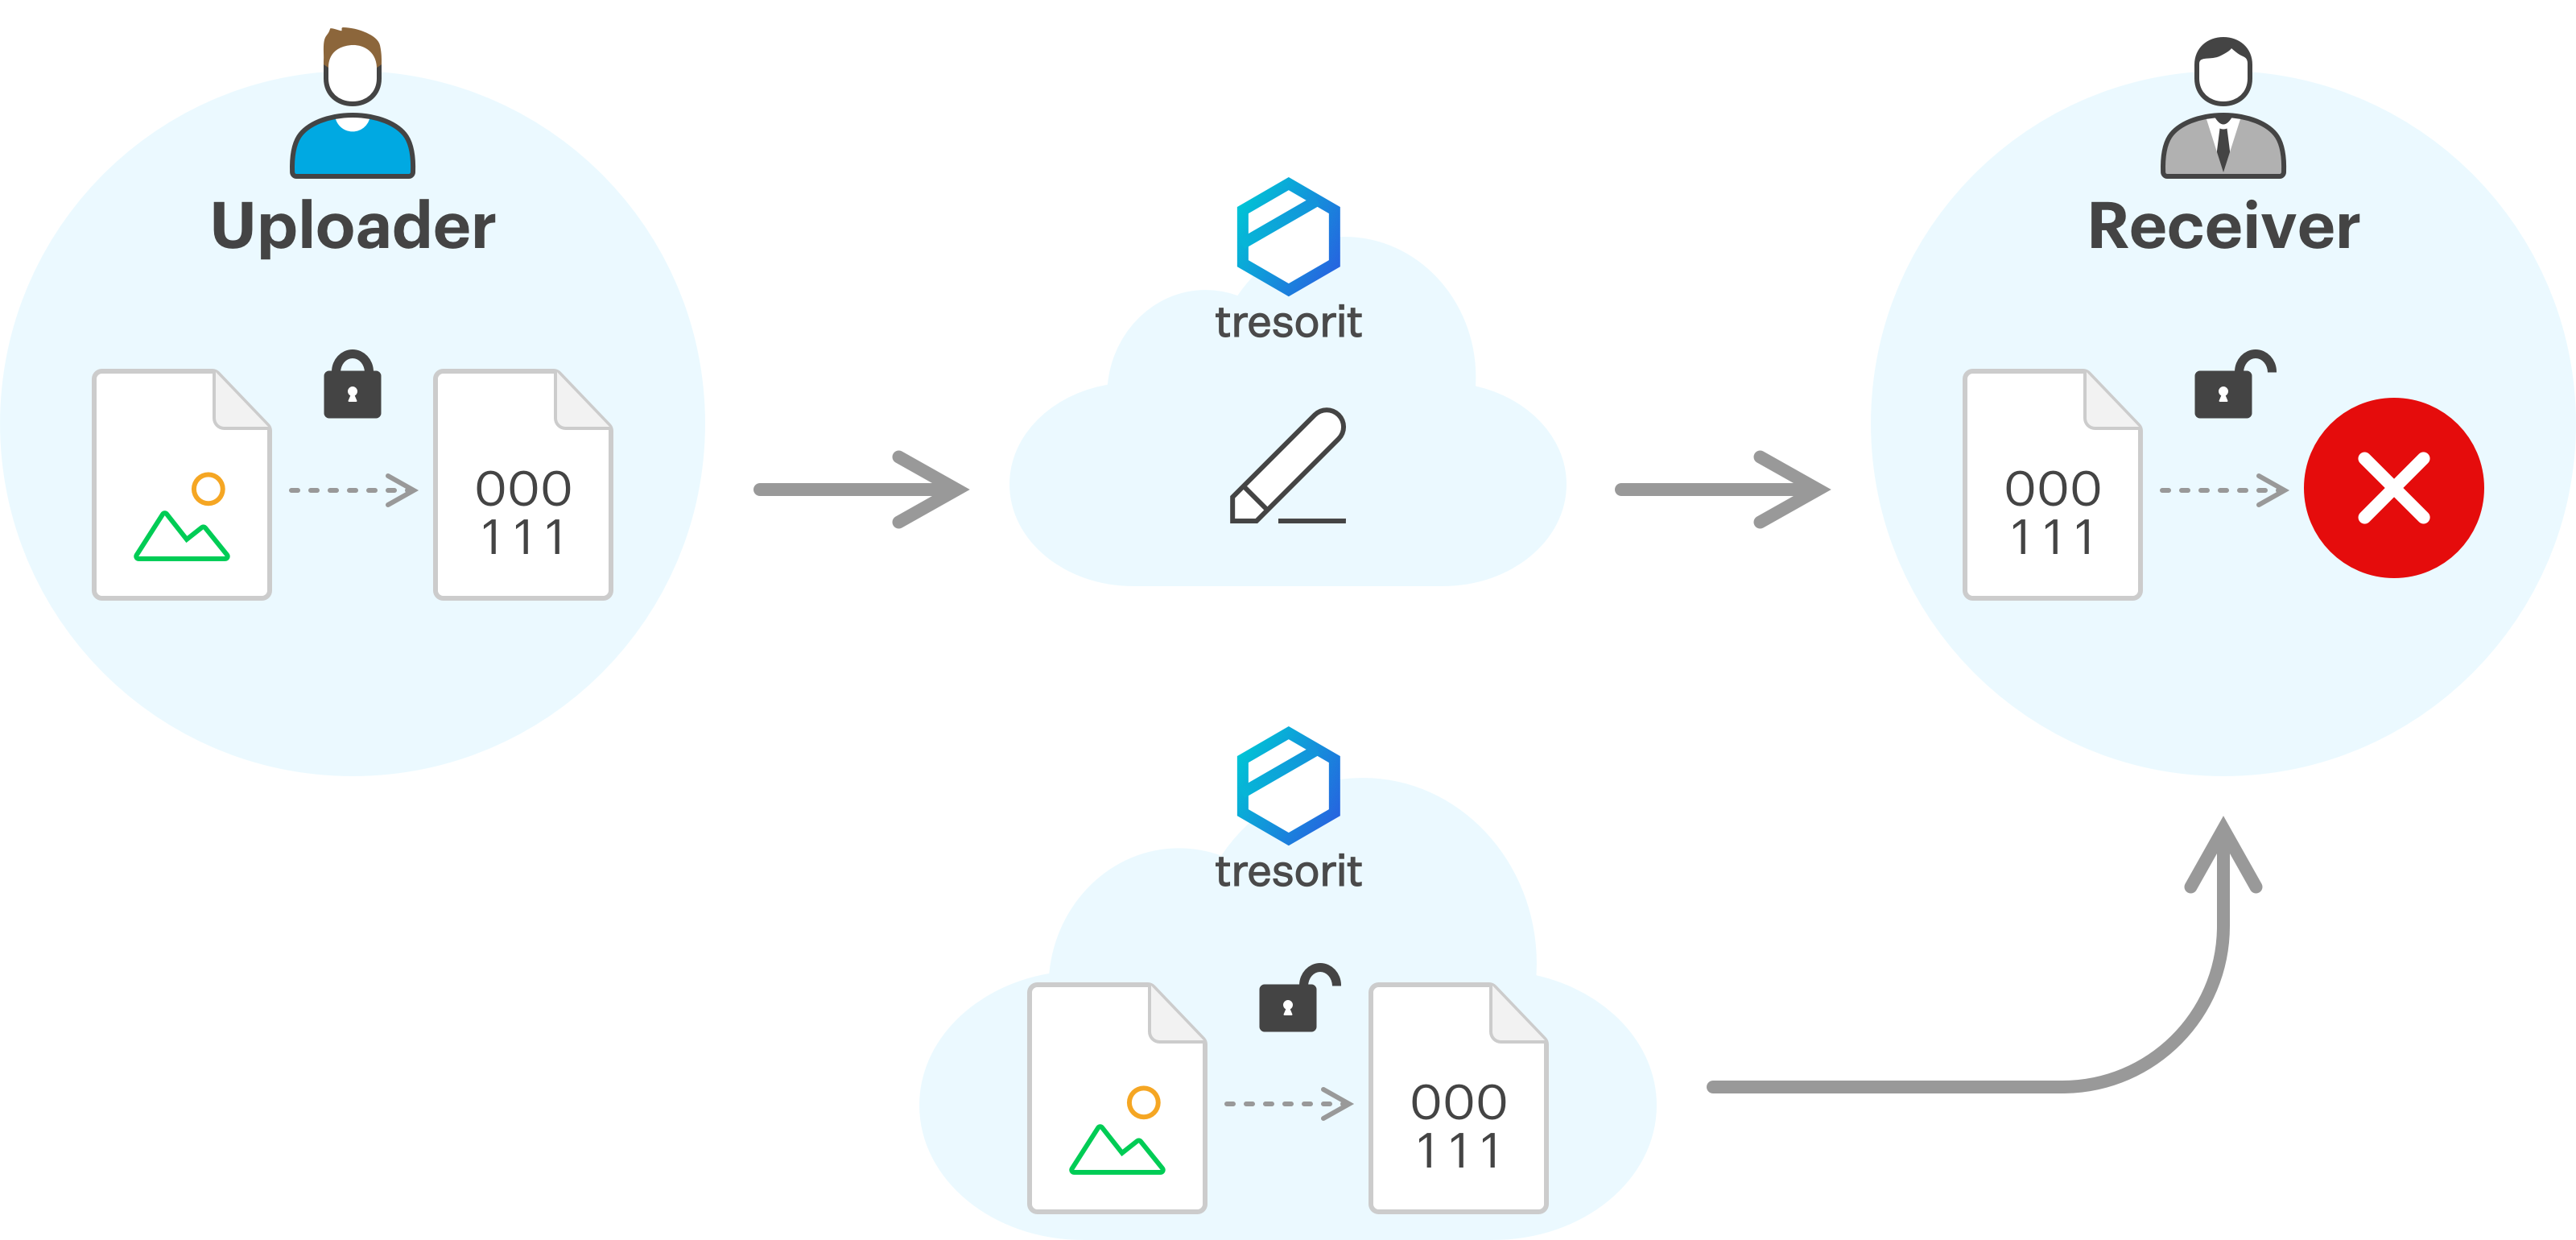
- Our servers should not be able to decrypt the data. 我们的服务器不应能够解密数据。
- The uploader should be sure that the data is only accessible to the link sender. 上传者应确保仅链接发送者可以访问数据。
- The receiver should be able to verify that the uploader’s email address or the data wasn’t changed by the server. 接收者应该能够验证服务器没有更改上传者的电子邮件地址或数据。
- The server should not be able to “fake” uploads. 服务器不应能够“伪造”上传。
版权声明:本文内容由互联网用户自发贡献,该文观点仅代表作者本人。本站仅提供信息存储空间服务,不拥有所有权,不承担相关法律责任。如发现本站有涉嫌侵权/违法违规的内容,请联系我们,一经查实,本站将立刻删除。
如需转载请保留出处:https://51itzy.com/kjqy/76629.html