
1、vsftpd的简介
vsftpd是“very secure TTP daemon”的缩写,是一个完全免费的、开放源代码的ftp服务器软件
2、特点
vsftpd是一款在Linux发行版中最受推崇的ftp服务器程序,小巧轻快,安全易用,支持虚拟用户,支持带宽限制等功能
3、安装
检查Linux系统是否安装了vsftpd的命令:rpm -qa|grep vsftpd
卸载vsftpd的命令yum remove vsftpd
执行yum -y install vsftpd
[root@localhost ~]# yum -y install vsftpd
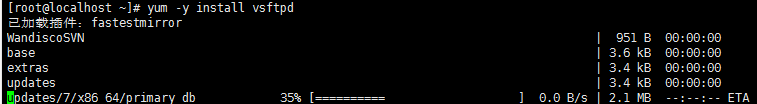
使用whereis vsftpd 查看安装路径
[root@localhost ~]#whereis vsftpd

注:
(1)是否使用sudo权限执行,请根据具体环境决定
(2)yum安装vsftpd的默认配置文件在/etc/vsftpd/vsftpd.conf
4、创建虚拟用户
(1)选择在根目录或用户目录下创建ftp文件目录:mkdir ftpfile,如/ftpfile,
[root@localhost ~]# cd /
[root@localhost /]# mkdir ftpfile
[root@localhost /]# ls
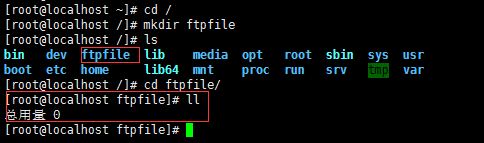
通过ftp上传时就会传到这个文件夹下
(2)添加匿名用户:useradd ftpuser -d /ftpfile/ -s /sbin/nologin #添加用户没有登录机器的权限,只有上传ftpfile有权限.(ftpuser 表示添加的自定义虚拟用户)
[root@localhost ftpfile]# useradd ftpuser -d /ftpfile/ -s /sbin/nologin
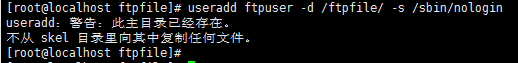
(3)修改ftpfile权限:chown -R ftpuser.ftpuser /ftpfile/ #把创建的用户和创建的文件夹的权限对应上。-R表示遍历,把用户或者用户组赋予到/ftpfile这个文件夹的权限上
[root@localhost ftpfile]# chown -R ftpuser.ftpuser /ftpfile/

查看该文件目录的权限(在文件所在目录执行)
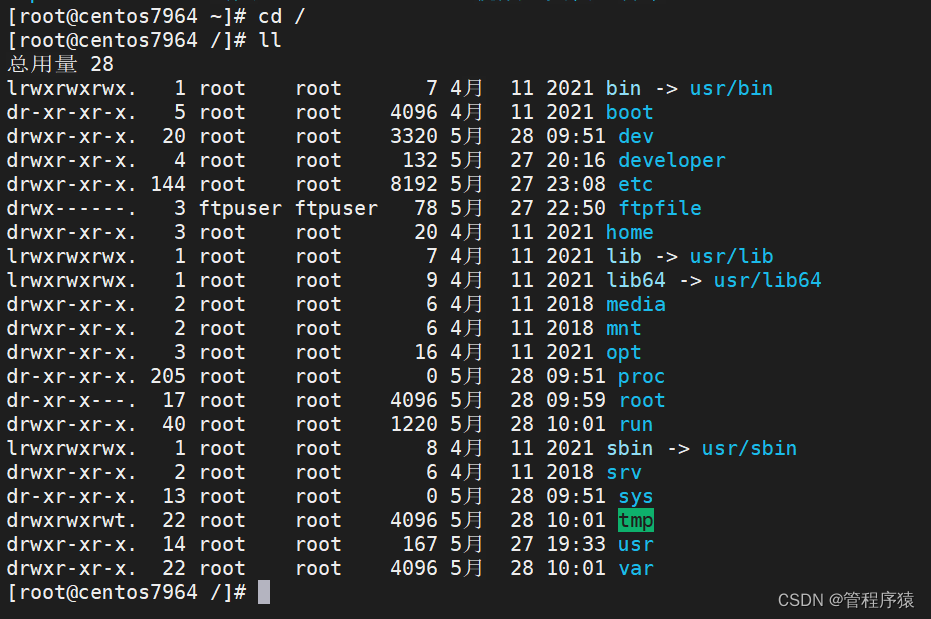
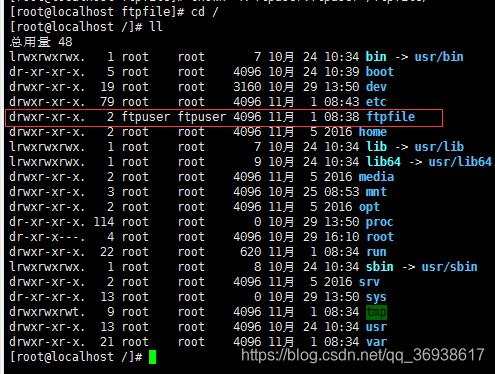
此时的用户名和用户组的权限都为ftpuser
[root@localhost /]# passwd ftpuser
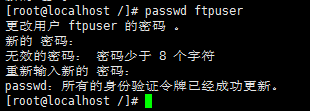
[旧笔记]
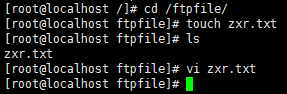
(5)在vsftpd文件目录下创建测试文件zxr.txt
[root@localhost /]# cd ftpfile/
[root@localhost ftpfile]# touch zxr.txt
[root@localhost ftpfile]# ls
zxr.txt
[新版本]
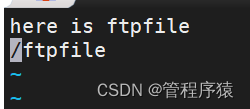
vim index.html
cd /ftpfile

添加内容:
5、vsftpd服务器的配置
(需要将vsftpd安装时候的目录指向刚才自定义的目录)
(1)vsftpd.conf文件
查看ftp服务器的安装路径【属于默认安装目录】
[root@localhost ftpfile]# whereis vsftpd

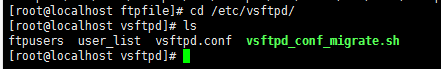
进入/etc/vsftpd/目录下[配置文件目录]
[root@localhost ftpfile]# cd /etc/vsftpd/
ja
编辑vsftpd.conf文件,把创建的用户配置上
修改:(在vsftpd.conf)
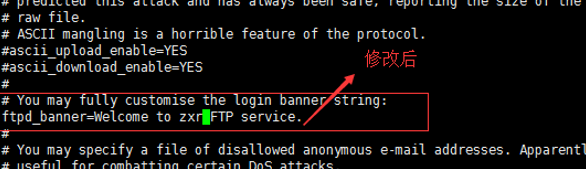
修改客户端登录,提示的欢迎信息(vi打开文件输入/然后将banner输入,再点击enter键,能快速找到banner信息)
ftpd_banner=Welcome to happymall FTP service. 讯享网
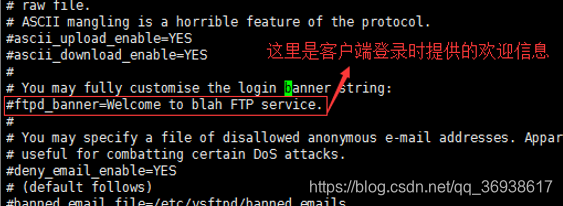
需要将注释取消掉,改为自己想要的提示信息
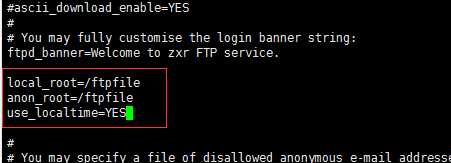
新增:(在vsftpd.conf)
还需要添加一些重要的属性节点
local_root=/ftpfile
anon_root=/ftpfile
use_localtime=YES
local_root=/ftpfile #把本地账户指向创建的ftpfile文件夹
anon_root=/ftpfile #添加匿名账户访问ftpfile目录
use_localtime=YES #ftp服务器用到的是本地的时间
修改:(在vsftpd.conf)
查找chroot_list节点
#chroot_local_user=YES #不激活,注释掉
chroot_list_enable=YES #激活
chroot_list_file=/etc/vsftpd/chroot_list #激活
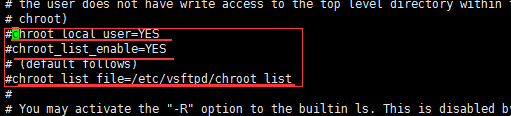
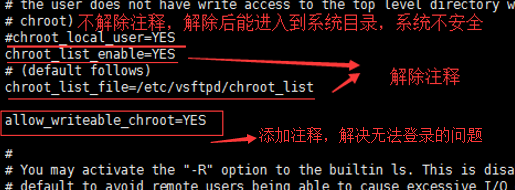
#chroot_local_user=YES #这个节点为是否锁定创建的/ftpfile为根目录,不解除注释,默认为chroot_local_user=NO,锁定创建的/ftpfile为根目录,如果解除后设置为chroot_local_user=YES,那么就没有锁定创建的/ftpfile为根目录,在命令行是可以访问到/ftpfile的上级目录,也就是系统的根目录,这是绝对不安全的。所以这个节点不用解除注释,或者解除更改为chroot_local_user=NO。
编辑该节点,解除
chroot_list_enable=YES
chroot_list_file=/etc/vsftpd/chroot_list
添加节点
allow_writeable_chroot=YES #加上这行解决了无法登陆的问题
两条命令的注释,将新建的用户添上。
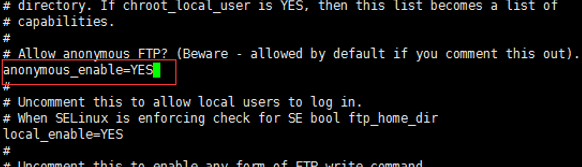
查找节点anonymous_enable
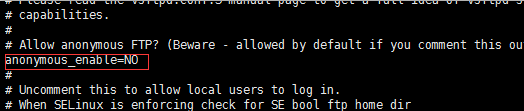
将该节点改为anonymous_enable=NO,不允许匿名用户登录
在该文件的末尾添加传输接口的范围,最大接口61001,最大接口62000,限定严格的设置防火墙。
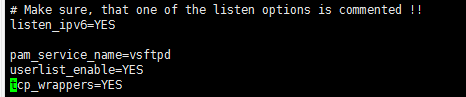
添加范围
pasv_min_port=61001
pasv_max_port=62000
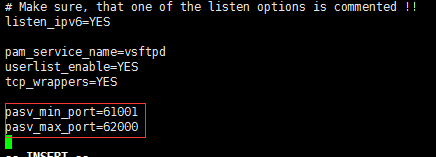
编辑完成保存退出。
(2)配置chroot_list文件
该文件目录的节点在上一步配置vsftpd.conf文件中已解除注释。
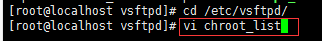
进入到/etc/vsftpd/目录下创建文件chroot_list
[root@localhost vsftpd]# cd /etc/vsftpd/
[root@localhost vsftpd]# vi chroot_list
#用编辑器打开文件时,如果没有这个文件,会默认自动创建一个该文件。
将用户添加进入该新建的chroot_list文件中
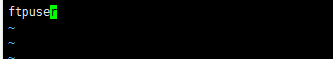
保存退出。
讯享网在 Example config file /etc/vsftpd/vsftpd.conf # # The default compiled in settings are fairly paranoid. This sample file # loosens things up a bit, to make the ftp daemon more usable. # Please see vsftpd.conf.5 for all compiled in defaults. # # READ THIS: This example file is NOT an exhaustive list of vsftpd options. # Please read the vsftpd.conf.5 manual page to get a full idea of vsftpd's # capabilities. # # Allow anonymous FTP? (Beware - allowed by default if you comment this out). anonymous_enable=YES # # Uncomment this to allow local users to log in. # When SELinux is enforcing check for SE bool ftp_home_dir local_enable=YES # # Uncomment this to enable any form of FTP write command. write_enable=YES # # Default umask for local users is 077. You may wish to change this to 022, # if your users expect that (022 is used by most other ftpd's) local_umask=022 # # Uncomment this to allow the anonymous FTP user to upload files. This only # has an effect if the above global write enable is activated. Also, you will # obviously need to create a directory writable by the FTP user. # When SELinux is enforcing check for SE bool allow_ftpd_anon_write, allow_ftpd_full_access #anon_upload_enable=YES # # Uncomment this if you want the anonymous FTP user to be able to create # new directories. #anon_mkdir_write_enable=YES # # Activate directory messages - messages given to remote users when they # go into a certain directory. dirmessage_enable=YES # # Activate logging of uploads/downloads. xferlog_enable=YES # # Make sure PORT transfer connections originate from port 20 (ftp-data). connect_from_port_20=YES # # If you want, you can arrange for uploaded anonymous files to be owned by # a different user. Note! Using "root" for uploaded files is not # recommended! #chown_uploads=YES #chown_username=whoever # # You may override where the log file goes if you like. The default is shown # below. #xferlog_file=/var/log/xferlog # # If you want, you can have your log file in standard ftpd xferlog format. # Note that the default log file location is /var/log/xferlog in this case. xferlog_std_format=YES # # You may change the default value for timing out an idle session. #idle_session_timeout=600 # # You may change the default value for timing out a data connection. #data_connection_timeout=120 # # It is recommended that you define on your system a unique user which the # ftp server can use as a totally isolated and unprivileged user. #nopriv_user=ftpsecure # # Enable this and the server will recognise asynchronous ABOR requests. Not # recommended for security (the code is non-trivial). Not enabling it, # however, may confuse older FTP clients. #async_abor_enable=YES # # By default the server will pretend to allow ASCII mode but in fact ignore # the request. Turn on the below options to have the server actually do ASCII # mangling on files when in ASCII mode. The vsftpd.conf(5) man page explains # the behaviour when these options are disabled. # Beware that on some FTP servers, ASCII support allows a denial of service # attack (DoS) via the command "SIZE /big/file" in ASCII mode. vsftpd # predicted this attack and has always been safe, reporting the size of the # raw file. # ASCII mangling is a horrible feature of the protocol. #ascii_upload_enable=YES #ascii_download_enable=YES # # You may fully customise the login banner string: ftpd_banner=Welcome to happymall FTP service. local_root=/ftpfile anon_root=/ftpfile use_localtime=YES # Beware that on some FTP servers, ASCII support allows a denial of service # # Beware that on some FTP servers, ASCII support allows a denial of service # # # You may specify a file of disallowed anonymous e-mail addresses. Apparently # useful for combatting certain DoS attacks. #deny_email_enable=YES # (default follows) #banned_email_file=/etc/vsftpd/banned_emails # # You may specify an explicit list of local users to chroot() to their home # directory. If chroot_local_user is YES, then this list becomes a list of # users to NOT chroot(). # (Warning! chroot'ing can be very dangerous. If using chroot, make sure that # the user does not have write access to the top level directory within the # chroot) #chroot_local_user=YES chroot_list_enable=YES # (default follows) chroot_list_file=/etc/vsftpd/chroot_list # # You may activate the "-R" option to the builtin ls. This is disabled by # default to avoid remote users being able to cause excessive I/O on large # sites. However, some broken FTP clients such as "ncftp" and "mirror" assume # the presence of the "-R" option, so there is a strong case for enabling it. #ls_recurse_enable=YES # # When "listen" directive is enabled, vsftpd runs in standalone mode and # listens on IPv4 sockets. This directive cannot be used in conjunction # with the listen_ipv6 directive. listen=NO # # This directive enables listening on IPv6 sockets. By default, listening # on the IPv6 "any" address (::) will accept connections from both IPv6 # and IPv4 clients. It is not necessary to listen on *both* IPv4 and IPv6 # sockets. If you want that (perhaps because you want to listen on specific # addresses) then you must run two copies of vsftpd with two configuration # files. # Make sure, that one of the listen options is commented !! listen_ipv6=YES pam_service_name=vsftpd userlist_enable=YES tcp_wrappers=YES pasv_min_port=61001 pasv_max_port=62000这里插入代码片
(5)编辑文件/etc/selinux/config文件
[root@localhost vsftpd]# vi /etc/selinux/config
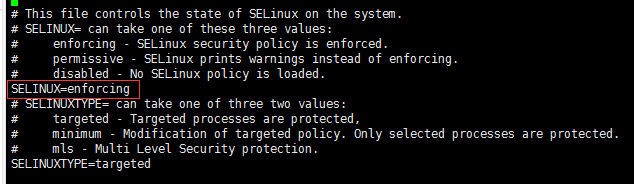
修改为SELINUX=disabled,如果不改的话,匿名账户无法创建文件文件或者文件目录
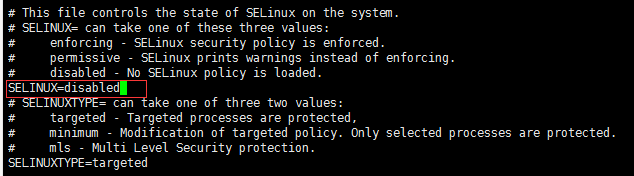
:wq保存退出
注:如果在验证的时候碰到550拒绝访问请执行:
sudo setsebool -P ftp_home_dir 1
然后重启Linux服务器,执行reboot命令。
6、vsftpd配置文件说明
sudo vi /etc/vsftpd/vsftpd.conf
vsftpd.conf文件的配置文件的添加或更新配置
本项目要用到的配置项:
1)local_root=/ftpfile(当本地用户登入时,将被更换到定义的目录下,默认值为各用户的家目录)
2)anon_root=/ftpfile(使用匿名登入时,所登入的目录)
3)use_localtime=YES(默认是GMT时间,改成使用本机系统时间)
4)anonymous_enable=NO(不允许匿名用户登录)
5)local_enable=YES(允许本地用户登录)
6)write_enable=YES(本地用户可以在自己家目录中进行读写操作)
7)local_umask=022(本地用户新增档案时的umask值)
8)dirmessage_enable=YES(如果启动这个选项,那么使用者第一次进入一个目录时,会检查该目录下是否有.message这个档案,如果有,则会出现此档案的内容,通常这个档案会放置欢迎话语,或是对该目录的说明。默认值为开启)
9)xferlog_enable=YES(是否启用上传/下载日志记录。如果启用,则上传与下载的信息将被完整纪录在xferlog_file 所定义的档案中。预设为开启。)
10)connect_from_port_20=YES(指定FTP使用20端口进行数据传输,默认值为YES)
11)xferlog_std_format=YES(如果启用,则日志文件将会写成xferlog的标准格式)
12)ftpd_banner=Welcome to mmall FTP Server(这里用来定义欢迎话语的字符串)
13)chroot_local_user=NO(用于指定用户列表文件中的用户是否允许切换到上级目录)
14)chroot_list_enable=YES(设置是否启用chroot_list_file配置项指定的用户列表文件)
15)chroot_list_file=/etc/vsftpd/chroot_list(用于指定用户列表文件)
16)listen=YES(设置vsftpd服务器是否以standalone模式运行,以standalone模式运行是一种较好的方式,此时listen必须设置为YES,此为默认值。建议不要更改,有很多与服务器运行相关的配置命令,需要在此模式下才有效,若设置为NO,则vsftpd不是以独立的服务运行,要受到xinetd服务的管控,功能上会受到限制)
17)pam_service_name=vsftpd(虚拟用户使用PAM认证方式,这里是设置PAM使用的名称,默认即可,与/etc/pam.d/vsftpd对应) userlist_enable=YES(是否启用vsftpd.user_list文件,黑名单,白名单都可以
18)pasv_min_port=61001(被动模式使用端口范围最小值)
19)pasv_max_port=62000(被动模式使用端口范围最大值)
20)pasv_enable=YES(pasv_enable=YES/NO(YES)
若设置为YES,则使用PASV工作模式;若设置为NO,则使用PORT模式。默认值为YES,即使用PASV工作模式。
FTP协议有两种工作方式:PORT方式和PASV方式,中文意思为主动式和被动式。
一、PORT(主动)方式的连接过程是:客户端向服务器的FTP端口(默认是21)发送连接请求,服务器接受连接,建立一条命令链路。
当需要传送数据时,客户端在命令链路上用 PORT命令告诉服务器:“我打开了端口,你过来连接我”。于是服务器从20端口向客户端的端口发送连接请求,建立一条数据链路来传送数据。
二、PASV(被动)方式的连接过程是:客户端向服务器的FTP端口(默认是21)发送连接请求,服务器接受连接,建立一条命令链路。
当需要传送数据时,服务器在命令链路上用 PASV命令告诉客户端:“我打开了端口,你过来连接我”。于是客户端向服务器的端口发送连接请求,建立一条数据链路来传送数据。
从上面可以看出,两种方式的命令链路连接方法是一样的,而数据链路的建立方法就完全不同。而FTP的复杂性就在于此。
)
7、防火墙的配置
防火墙的配置(这里采用的是centos6,用的还是Iptables文件设置防火墙)
(1)编辑防火墙文件
sudo vi /etc/sysconfig/iptables
(2)添加防火墙规则到配置文件中
-A INPUT -p TCP --dport 61001:62000 -j ACCEPT
-A OUTPUT -p TCP --sport 61001:62000 -j ACCEPT
-A INPUT -p TCP --dport 20 -j ACCEPT
-A OUTPUT -p TCP --sport 20 -j ACCEPT
-A INPUT -p TCP --dport 21 -j ACCEPT
-A OUTPUT -p TCP --sport 21 -j ACCEPT
(3):wq保存退出
(4)sudo service iptables restart 执行命令重启防火墙
8、vsftpd的验证
(1)执行sudo service vsftpd restart
[root@localhost vsftpd]# service vsftpd restart
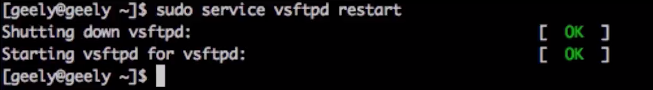
注:第一次启动时Shutting down vsftpd是failed不用理会,因为这是重启命令,保证Starting vsftpd for vsftpd是OK即代表vsftpd服务成功。、
service vsftpd stop #表示关闭vsftpd
(2)执行ifconfig查看运行vsftpd服务器的ip地址
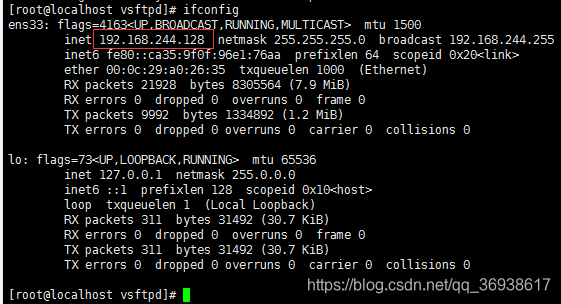
(3)打开浏览器访问:ftp://192.168.244.128/
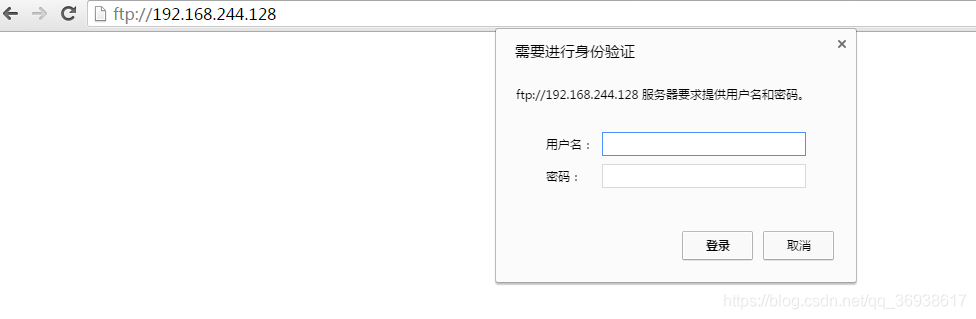
(4)输入之前创建的ftp匿名用户账号和密码
例如:用户名:ftpuser,密码:
(5)看到如图界面代表访问成功
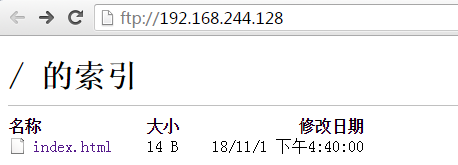
或者通过ftp客户端软件
例如:cuteftp、filezilla、viperftp、flashftp、leapftp等进行连接ftp服务器,进行上传文件、下载验证
9、vsftpd的常用命令
(1)启动:sudo service vsftpd start
(2)关闭:sudo service vsftpd stop
(3)重启:sudo service vsftpd restart
10、反复需要验证ftp身份问题解决
在安装vsftpd的时候如果在浏览器中一直提示需要身份验证,此时在命令行行登录会报530 Login incorrect错误。
在vsftpd的配置文件目录/etc/vsftpd下中的vsftpd.conf文件中会配置有pam_service_name=vsftpd指定pam下的文件在该文件中内容如下:
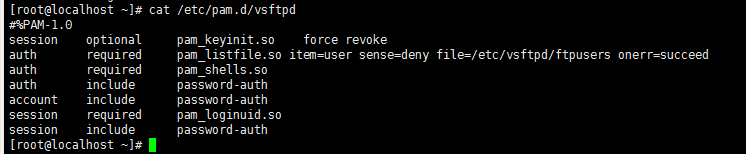
其中可能导致登录不成功(反复需要身份验证)的问题主要在于以下两个配置
问题配置一

在/etc/vsftpd/ftpusers这个文件中的用户是禁止登录的用户,先检查需要登录的账户是否在该文件中,如果在,就将该账户注释或者从该文件中去除
问题配置二:

该配置是允许用户的shell为 /etc/shells文件内的shell命令时,才能够成功
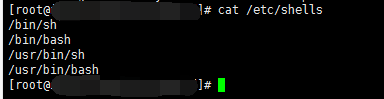
此处多留意有的系统里面的shells中的bash会多一些,比如
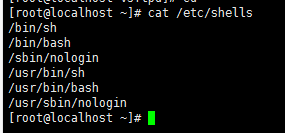
所以就需要查看当前系统shells文件中的内容与创建ftp用户的时候,为了禁止ssh登录,跟上的命令在shells中是否存在;
比如:我当前的shells文件内容为
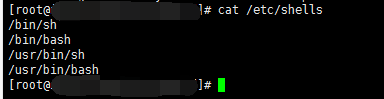
但是我在创建ftp用户的时候的命令为
[root@localhost ~]# useradd ftpuser -d /ftpfile/ -s /sbin/nologin
所以此时创建用户后-s /sbin/nologin并不是有效的。
这时的解决方案为修改/etc/pam.d/vsftpd文件中的
auth required pam_shells.so
修改为auth required pam_nologin.so
最后重启vsftpd
170.png)
所以就需要查看当前系统shells文件中的内容与创建ftp用户的时候,为了禁止ssh登录,跟上的命令在shells中是否存在;
比如:我当前的shells文件内容为
但是我在创建ftp用户的时候的命令为
[root@localhost ~]# useradd ftpuser -d /ftpfile/ -s /sbin/nologin
所以此时创建用户后-s /sbin/nologin并不是有效的。
这时的解决方案为修改/etc/pam.d/vsftpd文件中的
auth required pam_shells.so
修改为auth required pam_nologin.so
最后重启vsftpd
[root@localhost ~]# service vsftpd restart
版权声明:本文内容由互联网用户自发贡献,该文观点仅代表作者本人。本站仅提供信息存储空间服务,不拥有所有权,不承担相关法律责任。如发现本站有涉嫌侵权/违法违规的内容,请联系我们,一经查实,本站将立刻删除。
如需转载请保留出处:https://51itzy.com/kjqy/74209.html